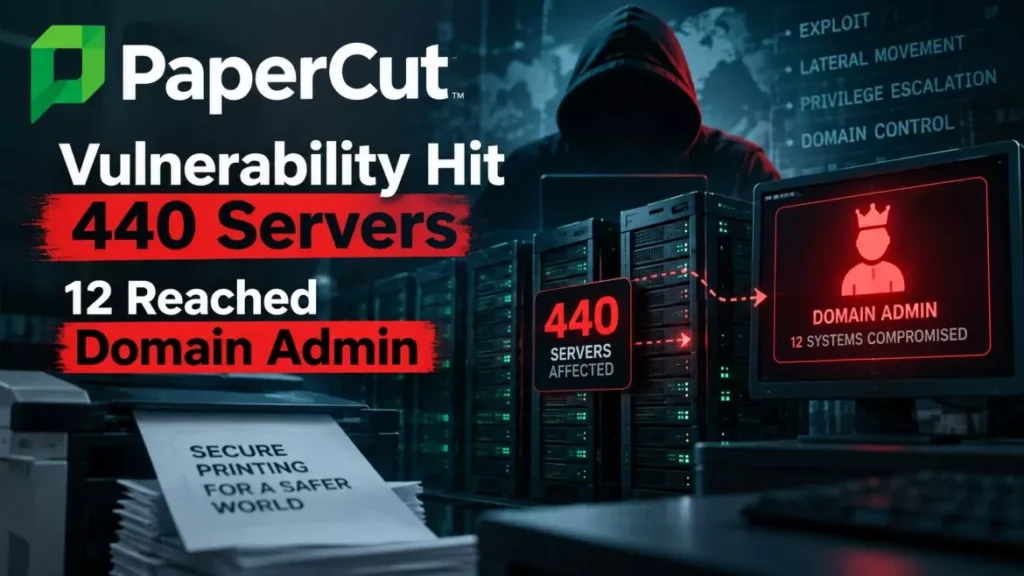
AI agents exploiting a PaperCut vulnerability compromised 440 servers at 395 organisations in 48 countries, the security firm GreyNoise reported on 10 September 2026. Only 12 of those organisations lost domain administrator control. PaperCut shipped tested maintenance releases the same day, and US federal agencies face a 14 September remediation deadline.
What the Campaign Did, in Numbers
The operation chained two flaws in PaperCut NG and PaperCut MF, print and document-management software that the vendor says is used by 139 million people at 89,000 organisations in 195 countries. GreyNoise says the campaign began on 31 August 2026 and that the operator went from an empty workspace to remote code execution on a real victim in under four hours.
| Measure | Count |
|---|---|
| PaperCut instances compromised | 440 |
| Victim organisations identified | 395 |
| Countries affected | 48 |
| Instances where credentials were harvested | 280 |
| Instances where operating-system or domain secrets were taken | 147 |
| Organisations where domain administrator was reached | 12 |
Education absorbed the most damage, with 204 victim organisations. By country, GreyNoise counted 98 victims in the United States, 59 in the United Kingdom, 31 each in France and Spain, and 24 in Canada. At the campaign’s peak, 11 organisations were compromised inside 26 seconds. One United States high school went from initial access to full domain administrative control in seven minutes.
Where the AI Actually Changed the Outcome
The AI changed the speed and the spread, not the depth. The operator ran hundreds of agents built on OpenAI’s Codex as an execution harness alongside a DeepSeek model, with orchestration software including AionUI and Hindsight, a tool that gives agents persistent memory. That machinery is what produced 11 compromises in 26 seconds.
What it did not produce was 440 domain takeovers. Domain administrator, the account level that controls every machine on a Windows network, was reached at 12 organisations out of 395 — under 4%. The fastest took five minutes, the slowest 144 minutes. Where the agents got that far, they used long-established routes: harvesting credentials from the LSASS process in Windows memory, exploiting the 2021 noPac flaws, or simply adding an account where the PaperCut service was already running with domain-admin rights.
Ordinary hardening also held. GreyNoise reported that at least one victim’s Cloudflare web application firewall blocked the exploitation attempts, and concluded that organisations are “not helpless against agentic attacks”. The novelty in this campaign is industrialised tempo against a known, patched flaw — not a new class of break-in.
The Two Flaws, and Which Releases Fix Them
The exploit chain uses an authentication bypass to reach a remote code execution bug.
- CVE-2026-81578: Missing authentication for a critical function in the web management interface, letting an unauthenticated remote attacker change certain system settings. Rapid7 scores it 8.8 (high) on CVSS version 4.0.
- CVE-2026-82078: Unsafe dynamic class loading in the database connection feature, allowing arbitrary Java code to run under the PaperCut server process. Rapid7 scores it 9.4 (critical).
PaperCut NG and MF versions 24, 25 and 26 are affected. The vendor published an urgent advisory on 27 August 2026, then shipped three emergency patches on 28 August and 1 September after researchers at watchTowr Labs found bypasses in the first fix.
Those emergency patches have now been superseded. On 10 September 2026 PaperCut released maintenance builds 26.0.5, 25.0.13 and 24.1.10, which it describes as “Regular Maintenance Releases (MR) that have gone through complete QA testing” containing every fix from emergency releases 1, 2 and 3 plus further hardening. The 26.0.5 release notes state that the build contains no database upgrade, which removes the most common reason server updates get deferred. Administrators using the external card or ID user-lookup database connection are told they will need to reconfigure it after updating.
The 14 September Deadline, and Who It Binds
The United States Cybersecurity and Infrastructure Security Agency, the federal body that catalogues flaws under active attack, added both CVEs to its Known Exploited Vulnerabilities catalogue on 31 August 2026 with a remediation due date of 14 September 2026.
That date is binding only on US federal civilian executive branch agencies, under Binding Operational Directive 26-04, “Prioritizing Security Updates Based on Risk”. It carries no legal force for private companies, schools or organisations outside the United States. The catalogue entry lists known ransomware use for both flaws as “Unknown”.
The catalogue’s required action allows agencies either to apply vendor mitigations or to discontinue use of the product where mitigations are unavailable. PaperCut’s own interim guidance for internet-facing application servers is to restrict web access to trusted IP ranges, such as internal corporate networks, using firewall rules.
What Is Still Unknown
GreyNoise attributes the campaign to a “likely Russian-speaking” actor. That is a language-based assessment, not an identification, and no government has attributed the campaign publicly.
The motive is also unresolved. GreyNoise says it cannot tell whether the operator is building access to sell on to others or intends follow-on activity such as data theft or ransomware. Separately, the agents were instructed to avoid 28 countries, among them Russia, China, Hong Kong, Thailand and Iran, and some struck targets in those countries anyway. GreyNoise wrote that it is “currently unclear why the [attacker’s] agents deviated”.
Readers tracking the wider pattern may find context in this site’s reports on the SAP OVERPASS vulnerability and on what the Meta Muse AI agent can access.
Frequently Asked Questions
What Is the PaperCut Vulnerability Being Exploited?
Two chained flaws in PaperCut NG and PaperCut MF: CVE-2026-81578, an authentication bypass in the web management interface, and CVE-2026-82078, an unsafe dynamic class loading flaw allowing remote code execution. Versions 24, 25 and 26 are affected.
Which PaperCut Version Fixes It?
PaperCut released maintenance builds 26.0.5, 25.0.13 and 24.1.10 on 10 September 2026. They replace the three emergency patches issued on 28 August and 1 September 2026.
How Many Organisations Were Compromised?
GreyNoise identified 395 victim organisations and 440 compromised PaperCut instances across 48 countries in its report published on 10 September 2026. Domain administrator control was reached at 12 of those organisations.
Is the 14 September 2026 Deadline Mandatory?
Only for United States federal civilian executive branch agencies, under CISA Binding Operational Directive 26-04. It has no legal force for private organisations or for bodies outside the United States.
Was Ransomware Deployed in the PaperCut Campaign?
Not established. CISA’s catalogue entry lists known ransomware use as “Unknown” for both flaws, and GreyNoise says it cannot determine whether the operator intends follow-on activity such as data theft or ransomware.