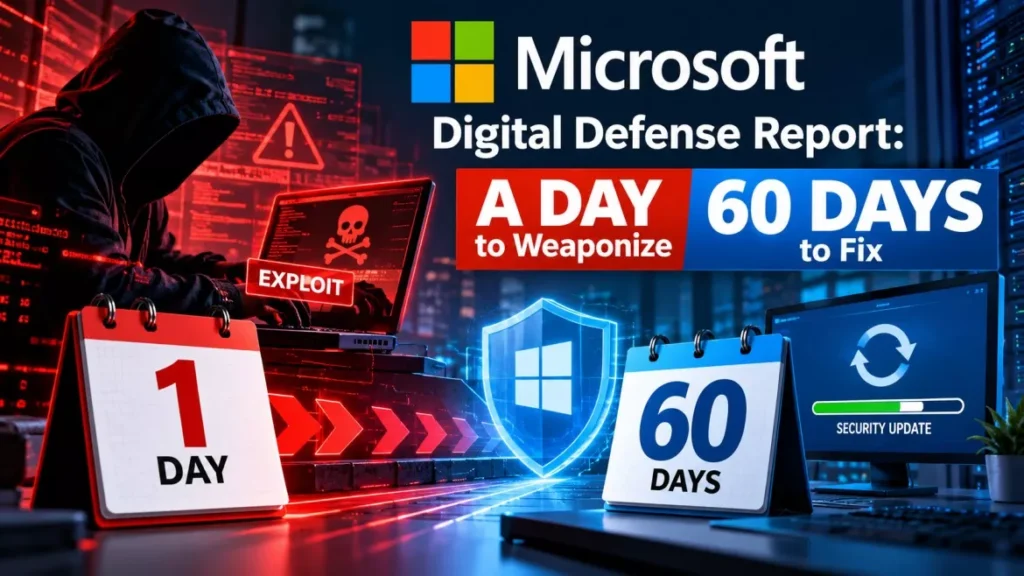
The Microsoft Digital Defense Report says the median time from a vulnerability being found in the wild to being weaponized has fallen to well below 24 hours. Microsoft puts enterprise remediation of critical external vulnerabilities at 30 to 60 days. The company published the 103-page report on 1 October 2026.
The Gap Between Weaponizing and Patching
The report’s central finding is a mismatch in speed, not a rise in attack volume. Microsoft, the Redmond software company that runs the Defender security platform, frames the whole document around it with the subtitle “AI is changing the physics of cybersecurity; Defense has to change with it”.
| Measure | Microsoft’s figure |
|---|---|
| Median time from discovery in the wild to weaponization | Well below 24 hours |
| Enterprise remediation of critical external vulnerabilities | 30 to 60 days |
| CVEs published in the first half of 2026 | Nearly 40,000 |
| Devices running attacker-supplied ClickFix commands, February to early May 2026 | More than 1.1 million |
Microsoft’s own description of the cause is blunt: finding and weaponizing a flaw once needed human expertise, and in many cases now comes down to “simply writing a prompt”. The figures published with the report put the nearly 40,000 CVEs recorded in the first half of 2026 on track to roughly double for the year; Help Net Security’s reading of the report puts the full-year estimate near 72,000.
Why Remediation Cannot Keep Up
Microsoft argues the lag is structural rather than a matter of effort. The report says remediation “is inherently much slower than discovery, not least because many systems lack robust unit and integration testing and so cannot deploy code changes rapidly”.
The consequence it draws is a forecast about backlog rather than about any single attack: “This means the world is likely to experience a multi-year period where the number of known but unpatched vulnerabilities spikes.”
Phishing Became the Fastest-Growing Way In
Phishing accounted for 23% of the intrusions Microsoft observed, against 7% a year earlier. Exploits against public-facing applications rose to 24% from 15% over the same comparison.
Two further figures describe what happens after the first foothold. In intrusions involving valid accounts, 52.2% went on to further credential theft, and 18.4% of intrusions involved an active password-spray campaign. Microsoft also notes that AI lets attackers personalise every message, which turns targeted spear phishing into something that can be run at scale.
The pattern matches what takedowns have shown in practice. The operation against one phishing kit last month did not undo the damage already done, as our report on the EvilTokens phishing takedown and 12,000 inboxes set out.
JADEPUFFER and the First Automated Extortion
The report identifies the point at which an AI-run attack stopped being hypothetical. In July 2026 the Sysdig Threat Research Team documented JADEPUFFER, described as the first confirmed fully automated ransomware extortion, in which the attacking system picked targets, issued the ransom demand and ran the extortion exchange with minimal human involvement.
Microsoft says it has since seen further AI-orchestrated intrusions with characteristics consistent with JADEPUFFER, at low volumes. It also records a shift over roughly six months “from AI assisting human operators, to AI directing attack activity, toward autonomous execution”, and notes one laboratory evaluation in which a frontier system strung 32 attack stages together.
Partly automated intrusion campaigns had already been documented against specific software. Our coverage of the PaperCut vulnerability and the agent-driven campaign behind it describes one such case from September 2026.
The Old Vulnerability Still Doing the Most Damage
The report’s most awkward number is not about AI at all. Among detections tied to the five leading CVEs, Microsoft found 58% were associated with a single vulnerability first disclosed in 2020, CVE-2020-1472.
That flaw, in the Windows Netlogon protocol, has had a patch available for roughly six years. Its continued dominance suggests the practical exposure for most organisations is still unpatched known software rather than novel machine-generated attacks.
What Microsoft Tells Organisations to Do
The report closes with six priorities rather than a product list:
- Strengthen identity: Harden authentication and limit standing privilege.
- Manage exposure continuously: Treat external attack surface as something monitored rather than audited periodically.
- Secure software dependencies: Account for what the organisation inherits from its supply chain.
- Extend controls to AI systems: Give agent identities and permissions the same governance as human accounts.
- Connect signals across environments: Correlate detection data rather than leaving it siloed.
- Plan for recovery: Assume disruption and rehearse restoring from it.
What the Report Stops Short of Claiming
As of 4 October 2026, this is the most recent edition of the report, and it is more careful than its coverage has often been. Microsoft states that “target selection, operational decision-making, and execution of the most complex intrusions remain manually driven in the majority of campaigns we observe”.
It puts the same point another way elsewhere: most observed campaigns still retain human direction, even where frontier systems have shown end-to-end autonomy in laboratories and early real-world cases. Microsoft’s forecast is explicitly about a near-term window, not a permanent reversal — it expects the balance between attackers and defenders to be re-established, while warning that defenders must move sharply in the meantime. The report draws on more than 165 trillion daily security signals and is also published as an eight-page executive summary.
Frequently Asked Questions
When Was the Microsoft Digital Defense Report Published?
Microsoft published the 2026 edition on 1 October 2026, as a 103-page report with a separate eight-page executive summary.
How Fast Are Vulnerabilities Being Weaponized?
Microsoft puts the median time from a vulnerability being discovered in the wild to being weaponized at well below 24 hours.
Has an AI Actually Run a Ransomware Attack on Its Own?
The report cites JADEPUFFER, documented by the Sysdig Threat Research Team in July 2026, as the first confirmed fully automated ransomware extortion. Microsoft says it has seen similar activity since, at low volumes.
Does Microsoft Say AI Now Runs Most Attacks?
No. The report states that target selection, operational decisions and execution of the most complex intrusions remain manually driven in the majority of campaigns Microsoft observes.
Which Vulnerability Accounted for the Most Detections?
CVE-2020-1472, a Windows Netlogon flaw first disclosed in 2020, accounted for 58% of detections among the five leading CVEs in the report.