Air Security disclosed Plugin4Shell on 17 September 2026, a zero-click flaw in the plugin systems of Claude Code, OpenAI Codex, GitHub Copilot and Gemini CLI. Anthropic fixed it in Claude Code 2.1.179 and OpenAI in Codex 0.146.0. Microsoft has shipped no fix, and Google will not patch Gemini CLI.
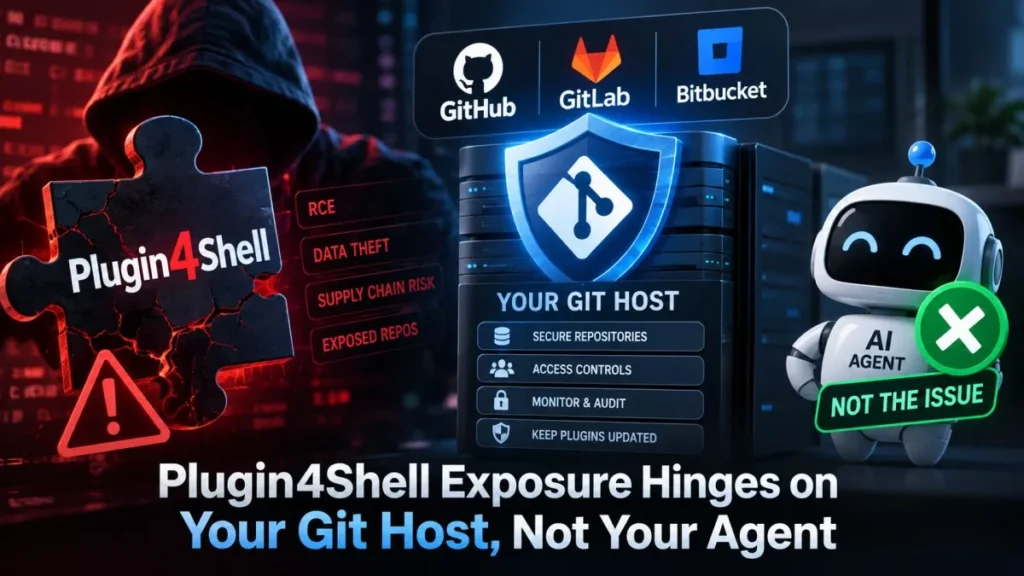
Plugin4Shell is not a flaw in any AI model. It is a flaw in how four coding agents install plugin code, and whether it can reach you depends on something most coverage has skipped: where the plugin repository is hosted.
Which Agents Are Fixed and Which Are Not
Two of the four affected agents are patched, one has no fix, and one will never get one. Air Security, the Israeli research lab that found the flaw, named three researchers on the disclosure: Or Nevo, Dor Granat and Niv Hoffman.
| Agent | Vendor | Status | Fixed version |
|---|---|---|---|
| Claude Code | Anthropic | Patched | 2.1.179 and later |
| Codex | OpenAI | Patched | 0.146.0 and later |
| GitHub Copilot | Microsoft | No fix shipped | None |
| Gemini CLI | Will not be fixed | None |
The timeline runs longer than the news cycle suggests. According to Air Security’s disclosure, the lab found the bug in May 2026, reported it to all four vendors in June 2026, logged Anthropic confirming the Claude Code 2.1.179 fix on 17 June 2026, verified the Codex 0.146.0 fix on 12 August 2026, and received word on 4 August 2026 that Google would not patch Gemini CLI.
As of 21 September 2026, no fix exists for GitHub Copilot, Microsoft has published no security advisory for the issue, and no CVE identifier has been assigned to Plugin4Shell. The researchers told Help Net Security they never received a reply from Microsoft; that account comes from the researchers and Microsoft has not publicly responded to it.
Why Your Git Host Decides Whether You Are Exposed
The single most useful fact about Plugin4Shell is that the main attack does not work on GitHub. GitHub refuses to create a branch whose name is a 40-character hexadecimal string, and that refusal is exactly what the attack needs.
All four agents let users add plugin marketplaces from any Git service, not only GitHub. The exposure therefore falls on plugins pulled from Bitbucket, GitLab installations and self-hosted Git servers, where nothing stops an owner from naming a branch after a commit hash. Teams that only ever install from the default GitHub-hosted marketplaces faced little practical risk from that variant, even before patching. Anyone running an internal plugin repository on their own Git server did.
There is one exception that breaks the rule. The Gemini CLI version of the attack uses a branch named FETCH_HEAD rather than a hash-shaped name, so GitHub’s restriction does not block it. Self-managed Git infrastructure has been a repeated weak point this month; a separate GitLab vulnerability disclosed on 10 September 2026 also hit self-managed servers hardest.
How the Attack Runs Without a Click
Plugin marketplaces pin each plugin to one reviewed version by its commit hash, a 40-character fingerprint of exact file contents. Plugin4Shell works because the agents ask Git for that commit but never check that the files they ended up with actually match it.
- Publish: An attacker releases a genuinely harmless plugin, pinned to a reviewed commit.
- Wait: Developers install it, and the marketplace review passes because the code really is clean.
- Update: The attacker ships a routine update and the marketplace re-pins to a new commit hash.
- Swap: The attacker creates a branch named after that new hash, pointing at malicious code, and makes it the repository default.
- Run: Git resolves the checkout to the branch instead of the commit, and the agent installs and runs the attacker’s code while still reporting the pinned version.
Nothing in that sequence asks the developer to approve anything, because plugin auto-updates run in the background by default in Claude Code and Codex. Air Security describes the outcome as full compromise of the agent and the machine it runs on, reaching whatever files, keys and repositories the agent can reach. The lab’s own summary claims millions of agents were affected; that figure is the researchers’ estimate and no vendor has published a count.
The correct fix is a single comparison after checkout: confirm that the commit Git actually landed on matches the pinned hash, and stop if it does not. Air Security notes that the check has to happen inside the agent, because a marketplace cannot enforce what a developer’s own Git client does. It is the same category of oversight as the BragJack attack on browser AI assistants: the trust boundary was assumed rather than verified.
How to Check Whether Your Agent Is Patched
- Claude Code: Run claude –version. Anything below 2.1.179 is vulnerable; update and re-run the check.
- Codex: Run codex –version. Anything below 0.146.0 is vulnerable.
- GitHub Copilot: No patched version exists, so check your plugin sources instead.
- Plugin sources: List the marketplaces you have added. Entries pointing at github.com are not exposed to the hash-branch variant; entries pointing at Bitbucket, a GitLab instance or a self-hosted server are.
- If you cannot patch: Remove plugin sources hosted outside GitHub, or disable plugins entirely until a fix ships.
Gemini CLI Is Gone for Most Users, but Not for All
Google’s answer to Plugin4Shell was that the product is on its way out, which is true for consumers and incomplete for everyone else. In its announcement on transitioning Gemini CLI to Antigravity CLI, Google said that “on June 18, 2026, Gemini CLI and Gemini Code Assist IDE extensions will stop serving requests” for Google AI Pro subscribers, Google AI Ultra subscribers, free Gemini Code Assist for individuals, and GitHub organisations using Gemini Code Assist.
The same announcement says access is unchanged for organisations holding a Gemini Code Assist Standard or Enterprise licence, and that Gemini CLI stays reachable through paid Gemini and Gemini Enterprise Agent Platform API keys. Those customers are running a tool that Google has confirmed it will not patch. Google’s recommended route out is Antigravity CLI, its replacement agent tooling.
What Is Still Unconfirmed
No one has reported Plugin4Shell being exploited in the wild. Air Security built working proof-of-concept exploits in May 2026 but has not claimed to have found an attack using them, and no breach, data loss or compromised plugin has been tied to the flaw by any vendor or researcher.
Microsoft has given no remediation date for GitHub Copilot and no public statement on the issue. Whether the flaw receives a CVE identifier, and what severity score it would carry, is also open. Pinning-and-verification failures of this kind are part of what national agencies are now trying to codify; South Korea’s internet security agency began drafting AI agent security guidelines earlier this month.
Plugin4Shell FAQ
What Is Plugin4Shell?
Plugin4Shell is a security flaw in the plugin installers of four AI coding agents. It lets whoever controls a plugin’s repository serve different code than the version the marketplace approved, and the agent runs it without asking the developer.
Which Versions Fix Plugin4Shell?
Claude Code 2.1.179 and Codex 0.146.0 both contain the fix, as do all later releases. GitHub Copilot and Gemini CLI have no patched version.
Is Plugin4Shell Being Exploited?
There is no public evidence of it. Air Security demonstrated the attack in a lab in May 2026, and as of 21 September 2026 no vendor or researcher has reported a real-world incident.
Are Plugins Hosted on GitHub Safe?
Largely, for the main variant. GitHub blocks branch names that look like commit hashes, which is the step the attack relies on. The separate Gemini CLI variant does not need such a name and is not blocked by that restriction.
What Should GitHub Copilot Users Do?
There is no patch to install, so the practical options are to remove plugin marketplaces hosted outside GitHub or to turn plugins off. Microsoft has not said when a fix will arrive.